
API Gateway & Rate Limiter
Custom proxy server featuring an in-memory sliding window rate limiter from scratch.
Security
Node.js Gateway
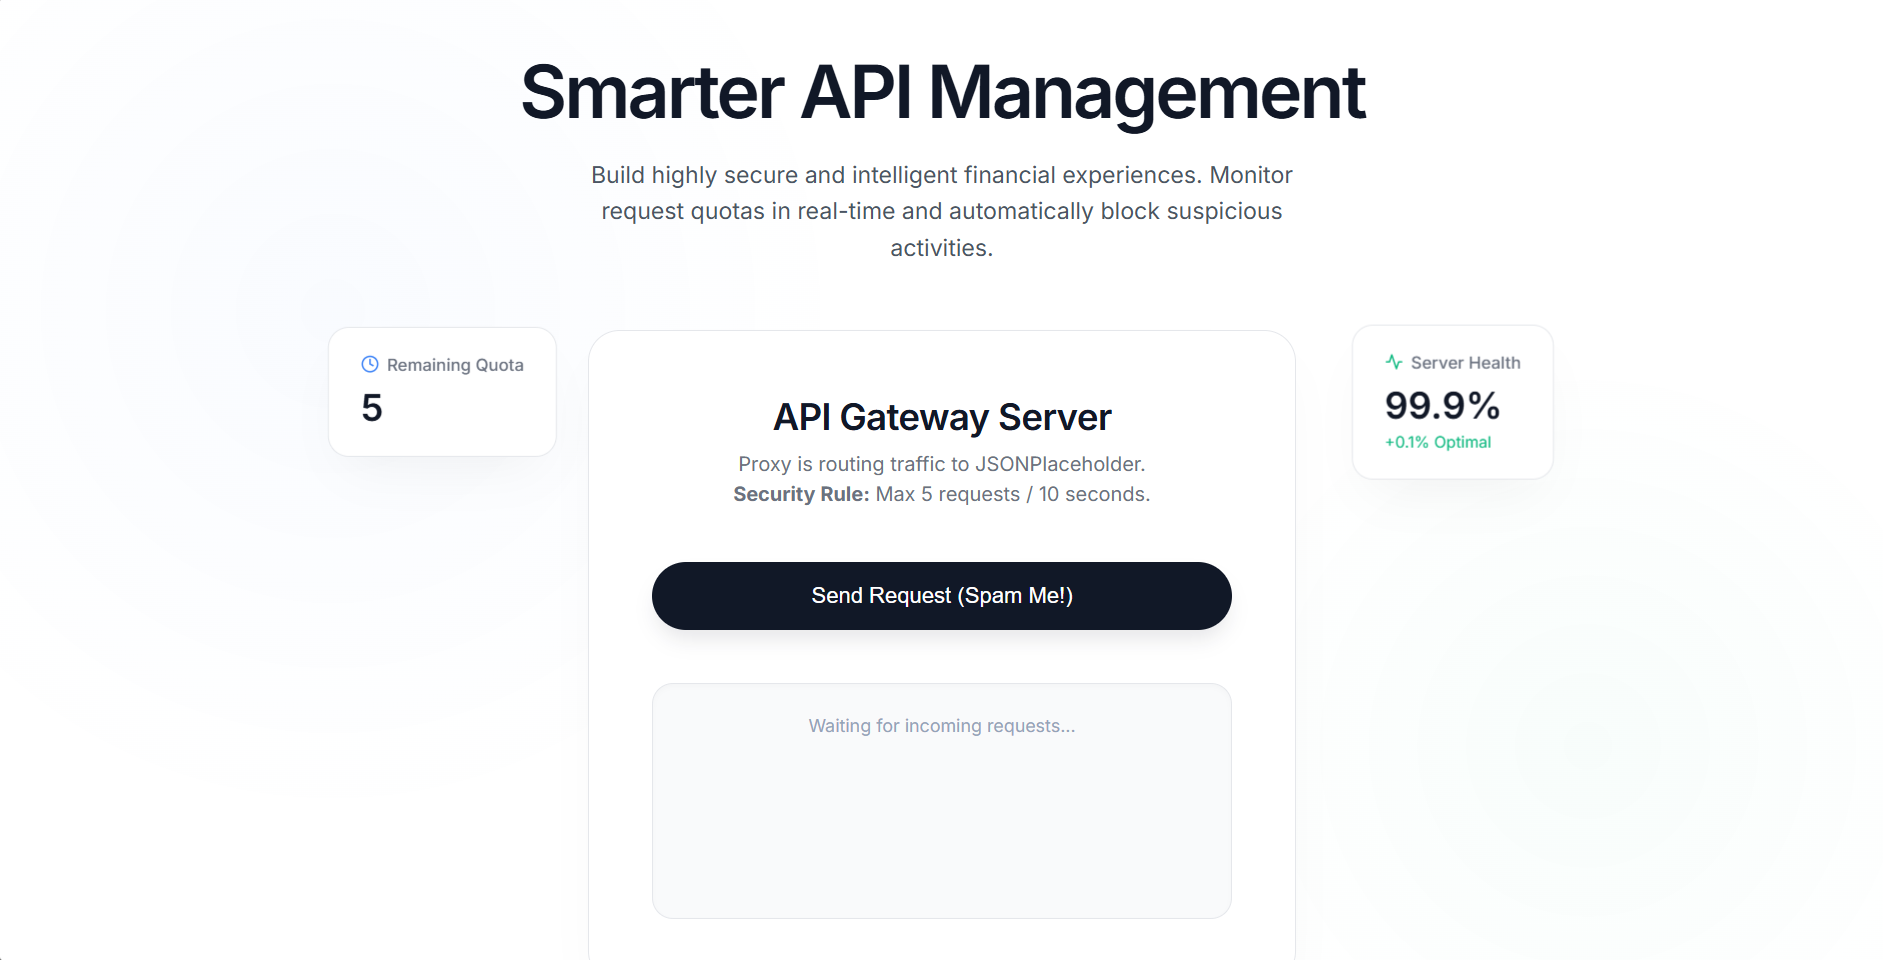
API Gateway & Rate Limiter — Custom Security Implementation
Built a custom proxy server in Node.js featuring an in-memory sliding window rate limiter from scratch, defending backend systems against spam and DDoS attacks.
This gateway acts as the central entry point for API requests, implementing strict rate limits based on client IP addresses using a highly efficient sliding window algorithm. It proxy passes valid requests to backend services while rejecting excessive requests.
Architecture
- Gateway: Node.js HTTP Server — Central routing and proxy mechanism
- Security Layer: Custom Sliding Window Rate Limiter — In-memory request tracking
- Target Systems: Simulated backend endpoints to validate rate limiting
Technologies
- Node.js
- Express.js (for proxying and routing)
- Custom Data Structures
Key Features
- Sliding Window Rate Limiting: High precision rate limiting that tracks requests over continuous time windows rather than discrete blocks.
- DDoS Protection: Prevents overwhelming backend systems by returning 429 Too Many Requests for abusive traffic.
- IP Tracking: Maintains in-memory stores mapping client IP addresses to request timestamps.
- Low Latency Proxy: Forwards valid requests with minimal overhead.
- Custom Error Responses: Clean JSON error formats with retry-after headers.
More Projects

Every project starts with a story. I turn those stories into digital experiences that feel effortless and expressive.